Responsible AI starts with governance: a practical guide for Adelaide businesses
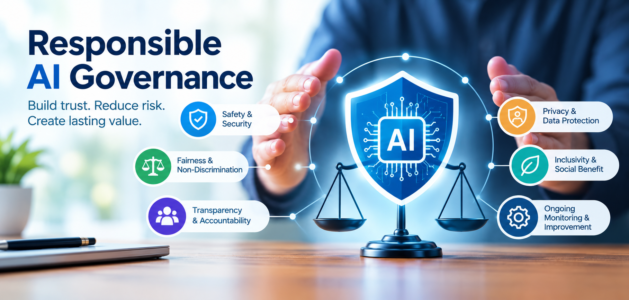
Ask most business leaders how to make AI responsible and the first answer is about technology: better models, better filters, better tools. In my experience the answer is closer to home. Responsible AI is mostly a governance job. It is about who is allowed to use AI for what, who is accountable when it goes wrong, and how you would know.
That is good news for a mid-sized Adelaide business or not-for-profit. You do not need a risk department, an ethics board or a six-figure consultancy. You need a handful of clear decisions, written down, owned by a named person and reviewed regularly. This article sets out how to do that in about an hour a month, for organisations that are using AI faster than they are governing it.
What governance actually means
Strip away the jargon and AI governance answers three questions:
- Who decides? Someone is accountable for how AI is used, and everyone knows who.
- What is allowed? There are simple, written rules about which tools may be used, for what, and with which data.
- How do we know it is working? The organisation checks, learns and fixes things, instead of hoping.
Responsible AI is the outcome: AI that is fair, safe, transparent and accountable. Governance is how you get there on purpose. It also connects to my earlier thinking on the need for Responsible AI.
The Australian Government’s Guidance for AI Adoption is a good yardstick. It sets out six essential practices: decide who is accountable, understand impacts, measure and manage risks, share essential information, test and monitor, and maintain human control. You do not need to adopt all of its detail on day one. The five steps below are a light-touch way to cover the same ground.
Five steps for a mid-sized business
1. Name one accountable owner. Pick a single executive, often the CIO, COO or a senior manager, who is accountable for AI use. Add a small group to advise: someone from IT, risk or compliance, HR and the business. Report to your board or leadership team quarterly. Without a name, nobody owns the problem.
2. List your AI. Create a simple register of every AI tool in use, including the ones staff adopted without asking. For each, record what it is used for, who uses it, what data goes in, who owns it and when it was last reviewed. Expect surprises. My article on shadow IT explains why staff turn to their own tools.
3. Write simple rules, scaled to risk. One page is enough to start. Say which tools are approved, what data must never be entered into public AI tools (the Office of the Australian Information Commissioner recommends that personal information is not entered into public generative AI tools), and when a human must check the output. Then sort uses into risk tiers, as shown below, so low-risk uses are not slowed by the same checks as high-risk ones.
4. Check your suppliers and your data. Most Adelaide businesses will buy AI, not build it. Ask each supplier where data is stored, whether your data is used to train their models, how long it is kept, how errors are handled and what happens if you leave. Put the answers in the register. Better still, write them into the non-functional requirements for the project, as I describe in my guide to non-functional requirements.
5. Test, monitor and review. Trial before you roll out, using your own real examples. Sample outputs each month. Let staff report problems without blame, and keep a short incident log. Review the register and rules every quarter, because tools and risks change quickly. Keep a way to pause or switch off any AI use that goes wrong.
A one-page starter: three risk tiers
| Tier | Example uses | Minimum controls |
|---|---|---|
| Low | Brainstorming, drafting internal text, summarising public information, with no personal or confidential data | Approved tool. The user checks the output and is accountable for it. |
| Medium | Drafting customer emails, summarising internal documents, searching policies | Business-approved tool with supplier checks. A person reviews before anything goes outside. Listed in the register. |
| High | Anything that affects a person’s job, credit, services, health or safety, or uses sensitive personal information | Owner sign-off, written risk assessment, testing on real cases, a human makes the final decision, affected people are told, and monitoring is in place. |
If a use does not fit a tier, treat it as high until someone has looked at it.
Making it work in Adelaide
Adelaide organisations face a particular set of limits, and governance has to fit them.
- A small talent pool. There are few specialist AI risk people in South Australia, and they are expensive. Build on people you already have: your risk, privacy, IT and HR staff. Add AI to an existing committee instead of forming a new one.
- Boards that need plain answers. A short quarterly report works better than a long paper: what AI is in use, what changed, what went wrong, and what decisions are needed. This builds on the cyber reporting ideas in my article on boards and cybersecurity.
- New privacy duties are close. From 10 December 2026, organisations covered by the Privacy Act must describe in their privacy policy the kinds of decisions made, or substantially supported, by automated programs that significantly affect people, and the personal information those programs use. The OAIC has published resources on transparency for AI and automated decision-making. Your AI register gives you most of what you need to write that statement.
- Useful public references. The South Australian Government publishes an Artificial Intelligence Ethics Policy and a guideline on generative AI for its own agencies. They are not binding on private organisations, but they are a good model if you work with government.
- Standards, when you are ready. ISO/IEC 42001 is an international standard for an AI management system, and it can be certified. For most mid-sized organisations it is a later step, after the five steps above are working.
Start small, start now
Governance does not slow AI down. It is what lets you say yes with confidence. Name an owner this week, build the register this month, and publish a one-page set of rules this quarter. Then keep reviewing, because the tools will keep changing.
What does AI governance look like in your organisation today? I would like to hear what has worked, and what has not.
